


NIS2 for healthcare: cybersecurity that fits your healthcare organisation [2026]
The NIS2 Directive (EU) 2022/2555 makes healthcare management bodies personally accountable for digital security under Article 20. Patient data, national identifiers, medical records: your data is among the most sensitive that exists. Lupasafe helps healthcare organisations become NIS2-compliant with one platform for people, technology and compliance.
Why NIS2 hits healthcare directly
Four developments that affect your healthcare organisation right now, regardless of your size.
Health is an "essential entity" sector
Under Annex I of the NIS2 Directive, the Health sector is listed among sectors of high criticality. Hospitals, mental-health institutions and healthcare organisations with 250+ employees or EUR 50M+ turnover qualify as "essential entities". Smaller organisations (50+ employees) qualify as "important entities". There is no transition period.
Management accountability
Article 20 of NIS2 requires management bodies to personally approve risk-management policies, oversee implementation and hold sufficient knowledge to assess risk. In cases of serious negligence, personal liability is possible.
24-hour reporting obligation
Significant incidents must be reported within 24 hours, followed by updates and a final report. This requires a working incident-management process, something many healthcare organisations have not yet operationalised.
ISO 27799 alone is not enough
A common misconception: "we have a healthcare information-security standard in place, so we are done". Standards like ISO 27799 form a solid baseline, but NIS2 adds a legal and governance layer: management accountability under Article 20, supply-chain security, incident reporting and demonstrable evidence.
"Lupasafe delivers half of our NIS2 action plan and saves a huge amount of work."
Marco Wientjes
IT Manager, Zorggroep Solis
Trusted by 600+ organisations



 ★★★★★5.0
 NIS2 partner
 Horizon 2020
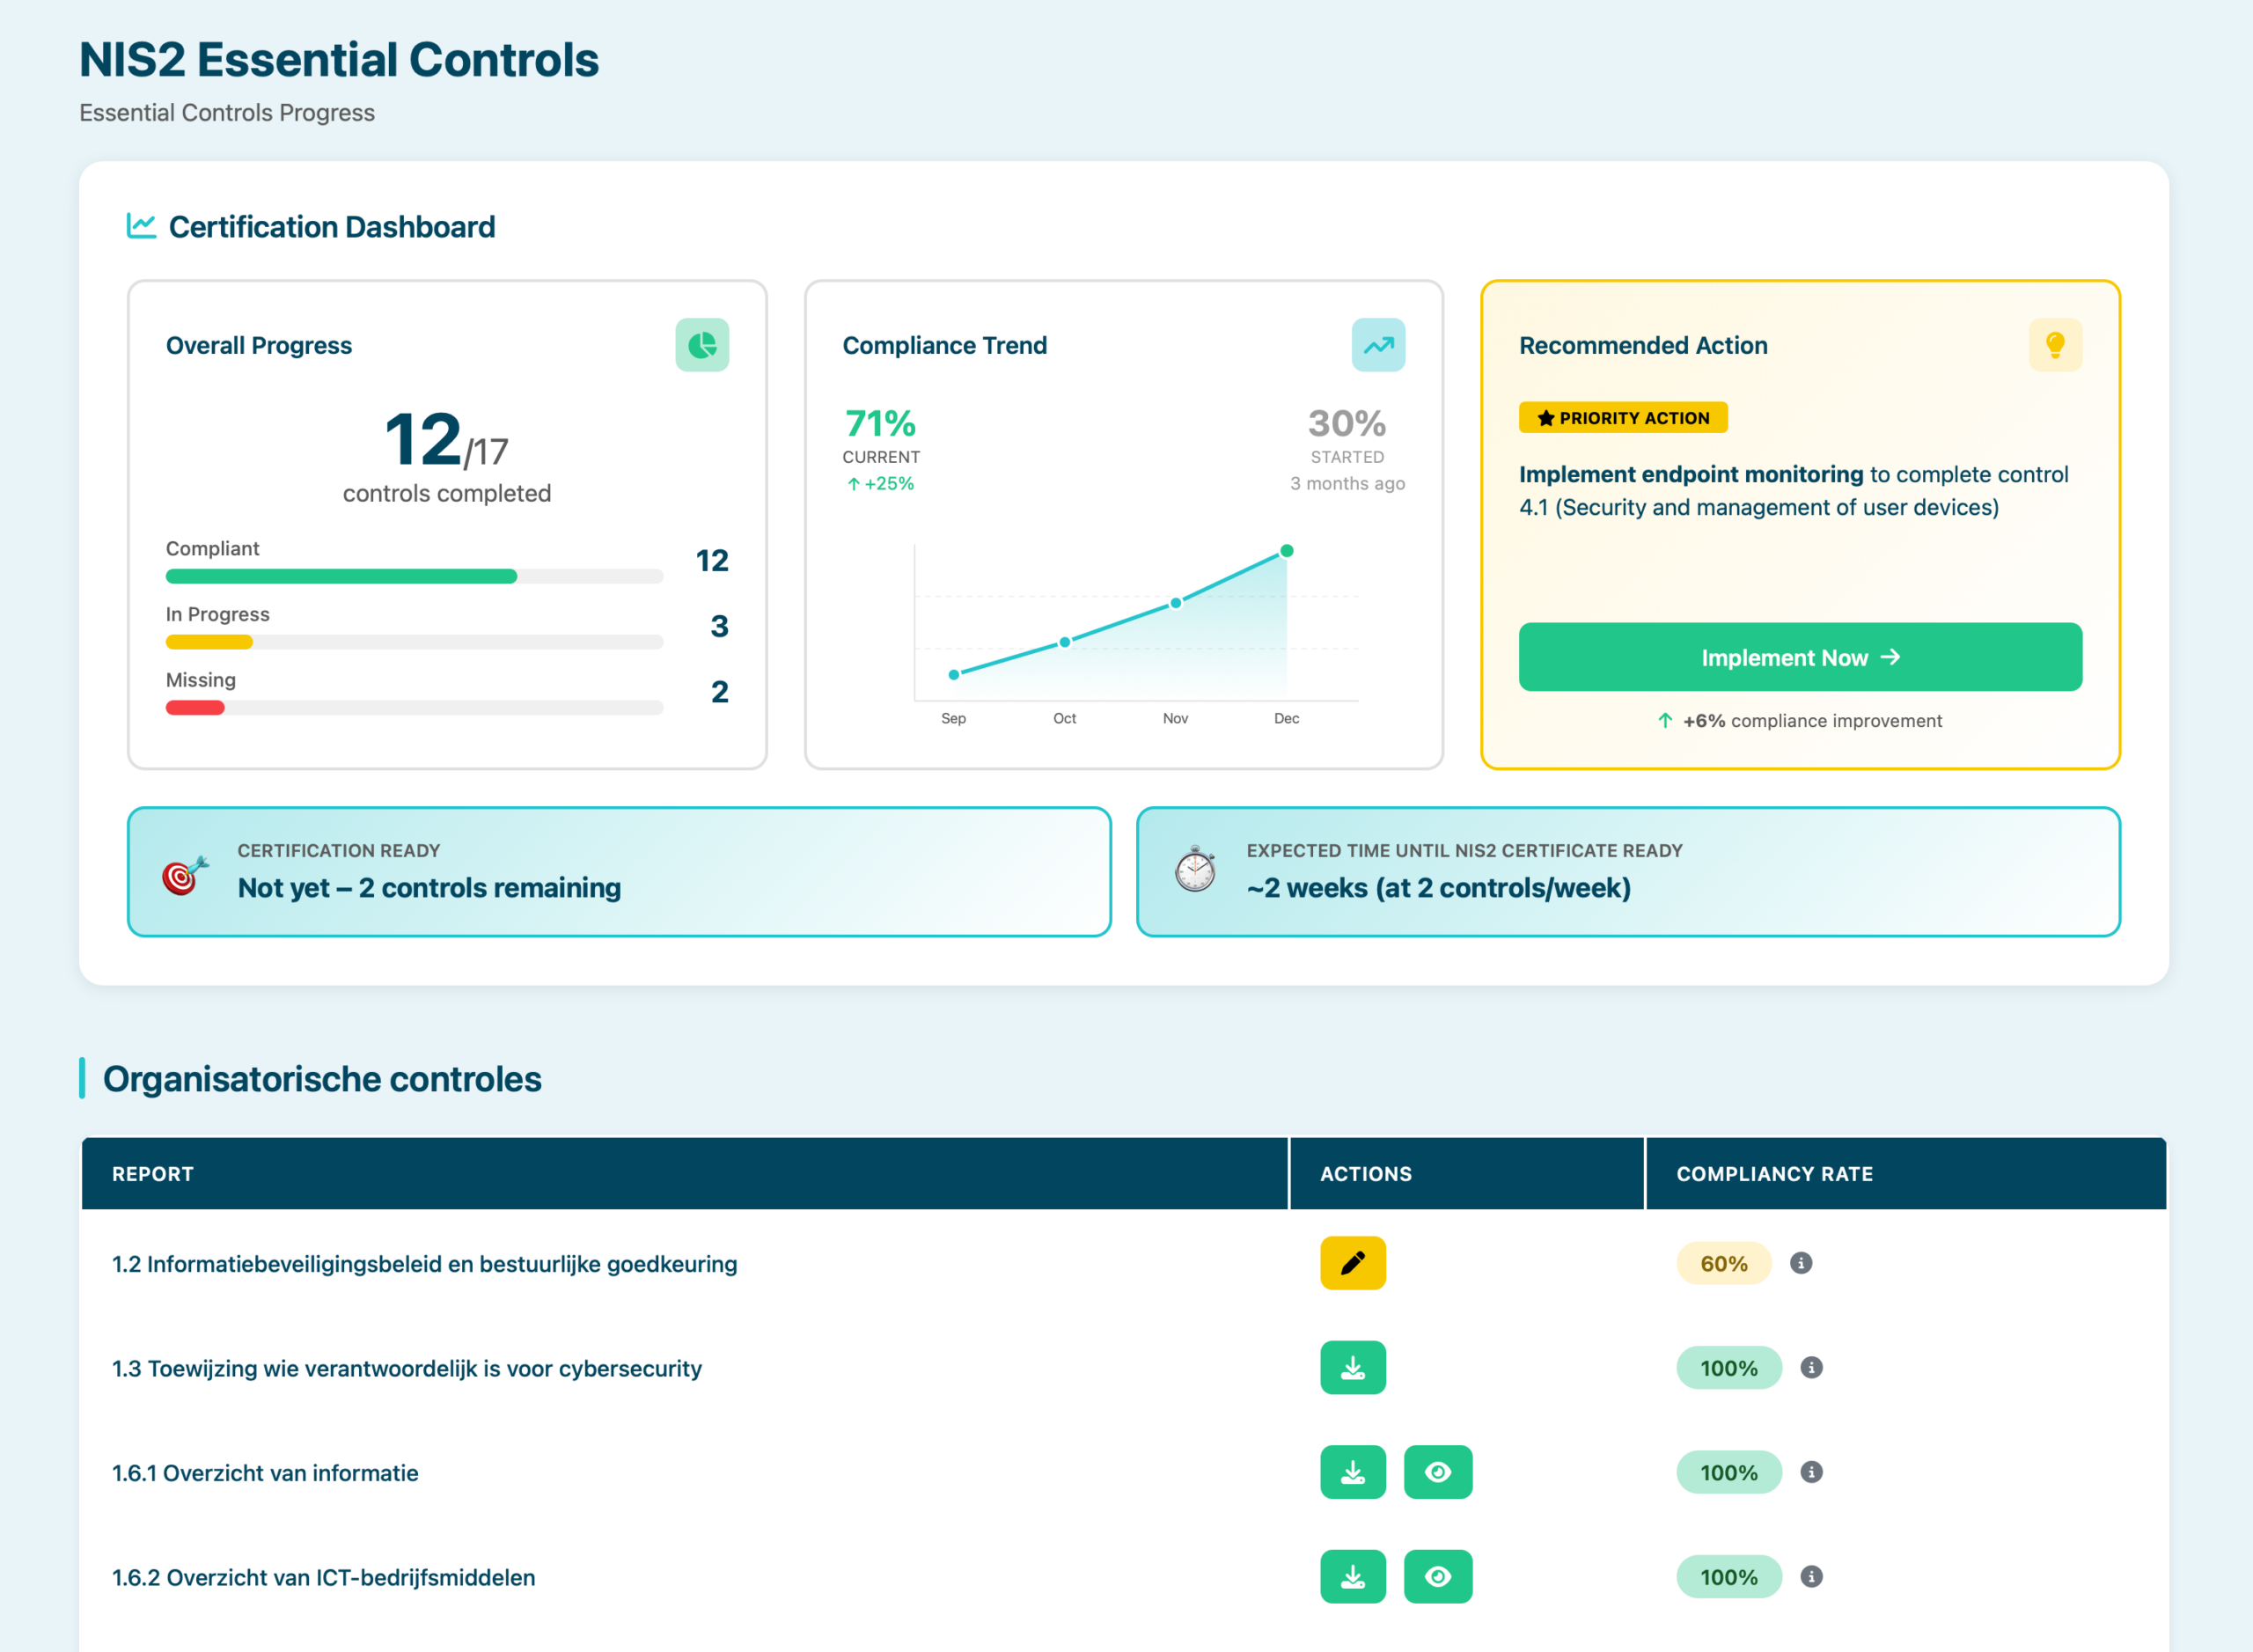
One dashboard for the key NIS2 risk-management measures
Lupasafe covers the cybersecurity risk-management measures of Article 21 of the NIS2 Directive (EU) 2022/2555. One platform for people, technology and compliance, complementing your healthcare information-security baseline. Insight into your status within 60 minutes.
Current status
Green, amber or red on every risk-management measure. No surprises at audit time.
Progress over time
Month over month, see how your maturity improves. Evidence for auditors and supervisory authorities.
Next best action
Exactly what you need to do to become audit-ready. No guesswork, no spreadsheets.
One place for all documents and evidence. Share with every stakeholder (healthcare institution, IT partner, consultant) and download everything for your auditor. One source of truth.
See the complete NIS2 checklist with the key risk-management measures →
Everything you need, deeply integrated
No disconnected tools. Every module automatically feeds your compliance dashboard.
Security awareness and e-learning
36-month training curriculum with healthcare-specific scenarios: phishing targeting electronic health record systems, fake emails from health insurers, and social engineering at the reception desk. Integrated training for management bodies (NIS2 Article 20) and staff cyber hygiene (Article 21(2)(g)), plus secure remote work (Article 21(2)(j)).
More on awareness training →Phishing simulations
Quarterly simulations with scenarios healthcare staff actually recognise: fake test results, requests for credentials to patient portals, urgent "IT updates". Includes QR-code phishing and SMS phishing for staff with a business mobile.
More on phishing simulations →Healthcare organisations already working with Lupasafe
Zorggroep Solis
Zorggroep Solis uses Lupasafe for NIS2 supply-chain compliance. IT Manager Marco Wientjes: "Lupasafe delivers half of our NIS2 action plan and saves a huge amount of work." The platform automatically covers half of their NIS2 programme.
Actief Zorg
6,000+ employees, 27,000 end clients. Continuous phishing awareness and NIS2 compliance reporting at scale.
Your healthcare organisation?
Whether you are a mental-health institution, home-care provider, nursing home or hospital, Lupasafe adapts to your scale and risk profile. Start with a free 30-day evaluation.
Book a no-obligation demo →Why healthcare is extra vulnerable
Healthcare organisations are attractive targets for cybercriminals. Not because they are weak, but because their data is valuable.
- ✓ Patient data is the most valuable category on the black market
- ✓ National identifiers cannot be replaced and enable identity fraud
- ✓ Ransomware hits extra hard because downtime directly impacts care delivery
- ✓ Remote and hybrid work expands the attack surface
What healthcare organisations struggle with:
1. No dedicated cybersecurity team, IT handles it "on the side"
2. Many suppliers with access to systems and patient data
3. Legacy systems that cannot easily be patched
4. High workload, so staff click on phishing more quickly
Ready to make your healthcare organisation NIS2-proof?
Start with a free 30-day evaluation. No credit card required. Insight into your NIS2 status within 60 minutes. The key NIS2 risk-management measures directly covered, complementing your healthcare information-security baseline.
Run the NIS2 scan Start free evaluationRead more
NIS2 checklist for SMEs
10 steps every director should take now. Also relevant for healthcare boards.Read more →
Set up a NIS2 awareness campaign
Why NIS2 Article 20 governance training and Article 21(2)(g) cyber hygiene demand more than a single e-learning.Read more →
NIS2 supply-chain approach
The best approach to NIS2 supply-chain risk management.Read more →
